Free kit
IT Security Audit Checklist
120 audit checks across 12 control areas, plus an audit plan and findings log — ready for your next internal IT audit.
Everything you need to plan and run an internal IT security audit: a 120-point checklist you can tick through on site, and the templates to plan the audit, record findings and track corrective actions to closure.
An IT security audit is not a penetration test. A penetration test looks for holes in one target; an audit checks that the controls you say you have are in place, are followed and actually work, across the whole environment. This kit is built for that job.
What is inside
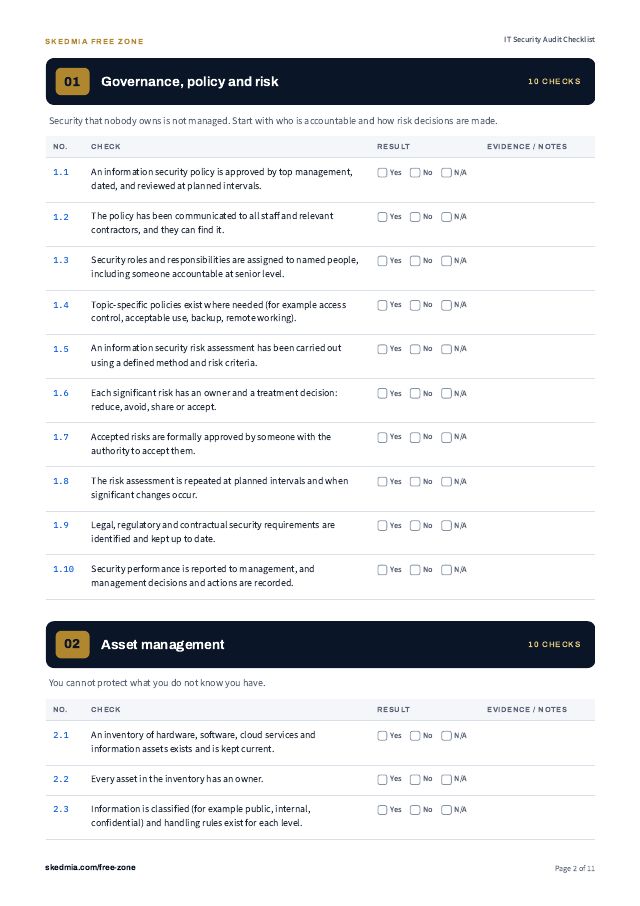
IT Security Audit Checklist — 120 checks in 12 control areas: governance and risk, asset management, identity and access, network security, endpoints and servers, vulnerability and patch management, data protection, logging and monitoring, incident management, backup and recovery, change and suppliers, people and physical security. Each check has Yes / No / N/A boxes and space for evidence.
IT Audit Plan and Findings Log — audit plan, risk-based scoping table, timetable, findings log with grading guidance, corrective action tracker and a report outline.
Both documents as a designed, print-ready PDF and as an editable Word file.
Who it is for
IT managers, internal auditors, information security officers and consultants — and anyone preparing for an ISO/IEC 27001 internal audit who wants a practical starting point.
How to use it
Plan the audit with the template, spend the most time where the risk is highest, and look for evidence for every check rather than accepting that something is done. For each No, write a finding that states the requirement, the evidence and why it does not conform, then agree an owner and a date.
What is in the kit
- IT Security Audit Checklist (PDF)120 checks in 12 control areas with Yes / No / N/A boxes and space for evidence. Print-ready.1.2 MB
- IT Audit Plan and Findings Log (PDF)Audit plan, risk-based scoping, timetable, findings log and corrective action tracker.585 KB
- IT Security Audit Checklist (editable Word)The same 120 checks in Word, so you can add your own and fill it in on screen.35 KB
- IT Audit Plan and Findings Log (editable Word)Editable templates — replace the text in [Square Brackets] with your own details.28 KB
A look inside
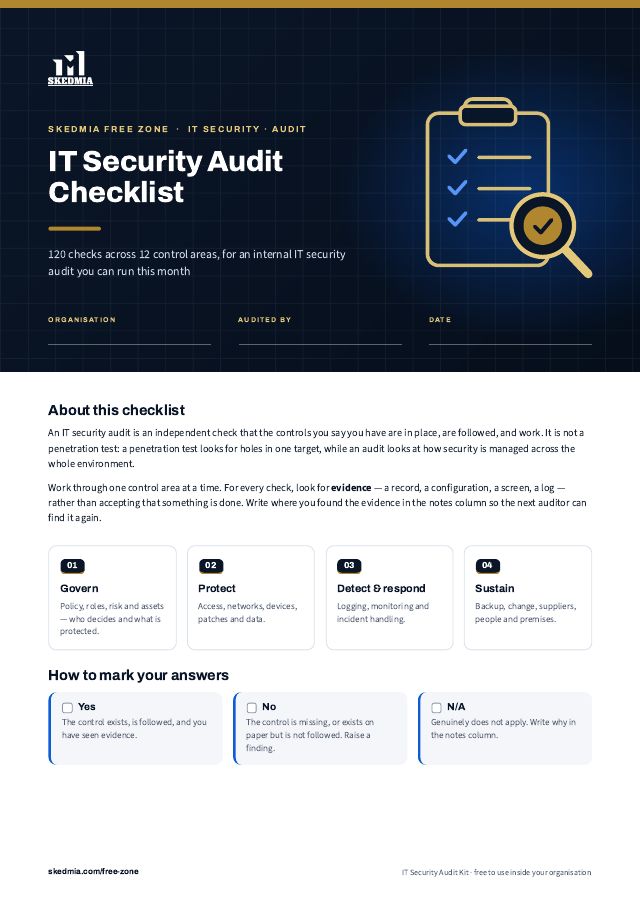
The first pages of IT Security Audit Checklist (PDF). The full document downloads from the list above.
Next step
Learn to use it properly — with a certificate
The documents tell you what to check. These courses teach you how to audit and implement it, online and at your own pace.
Questions people ask
Is the IT Security Audit Checklist really free?
Yes. There is no payment and no trial. Tell us your name, work email and company once, and every document in the Free Zone is yours to download.
What format are the documents in?
This kit has 4 documents in PDF and DOCX format. The Word, Excel or PowerPoint files are fully editable, so you can adapt them to your organisation.
Can I use it inside my company?
Yes. The licence covers one organisation with unlimited internal use — print it, share it with colleagues and adapt it. Please do not resell it or republish it as your own.
Does this make us compliant with ISO/IEC 27001?
No document can do that on its own. It is a practical working tool to help you prepare, check and improve. Conformity with ISO/IEC 27001 is decided by an audit of your actual system, and the standard itself remains the authoritative text.
Do you offer training on this topic?
Yes. Skedmia runs online courses with certificates on the standards and topics these kits cover — the matching courses are listed on this page.
More from the Free Zone
 FreeNewEditable
Cyber Security Risk Mitigation Checklist
80 controls in 10 risk areas, each with the reason it matters — plus a 5 × 5 cyber risk register template.
 FreeNewEditable
AWS Security Checklist
90 checks to review an AWS account — root user, IAM, network, S3 and databases, encryption, logging, detection and recovery.
 FreeNewPopular
ISO 27001:2022 Compliance Checklist
Check that your ISMS documents, clauses 4–10 and Annex A controls are audit-ready before certification.