Free kit
ISO 27701 Data Privacy and Cybersecurity Audit Guide
A 43-slide walk-through of ISO/IEC 27701:2019 for auditors: the PIMS, its link to GDPR, privacy impact assessment, the audit workflow, annexes and findings.
A structured slide guide to the privacy information management system (PIMS) standard and how it is audited. It explains what ISO/IEC 27701 adds to an information security management system, how it relates to GDPR, and how an audit moves from planning to findings.
What is inside
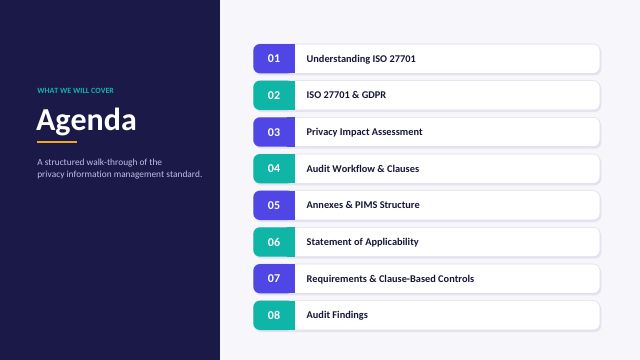
Understanding ISO 27701 — what a PIMS is and who the standard is for.
ISO 27701 and GDPR — how the two relate.
Privacy impact assessment.
Audit workflow and clauses.
Annexes and PIMS structure.
Statement of Applicability.
Requirements and clause-based controls.
Audit findings.
One PDF in widescreen slide format.
Who it is for
Internal auditors, data protection officers, information security managers and consultants who prepare for, carry out or receive a privacy audit against ISO/IEC 27701.
How to use it
Use it as a briefing before an audit: go through the audit workflow and clause sections with the audit team, then use the Statement of Applicability and controls sections to plan what evidence to sample. It also works as an awareness session for process owners who will be interviewed.
This is a training guide, not the standard. Requirements are summarised in our own words and the published standard remains the only authoritative text. This guide is written against the 2019 edition of ISO/IEC 27701; a newer edition has since been published, so check which edition your audit uses.
What is in the kit
- ISO 27701:2019 Data Privacy and Cybersecurity Audits (PDF)43 slides in eight parts, from understanding ISO 27701 and its link to GDPR to the audit workflow, Statement of Applicability and audit findings.271 KB
A look inside
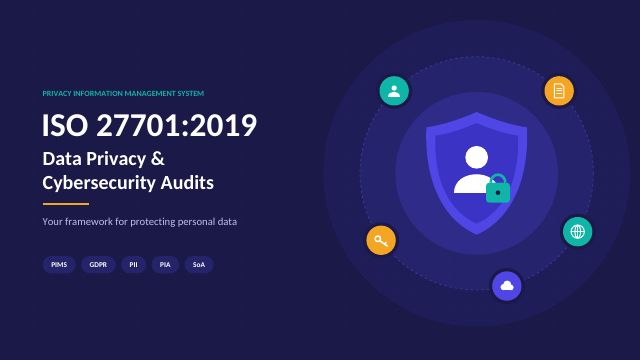
The first pages of ISO 27701:2019 Data Privacy and Cybersecurity Audits (PDF). The full document downloads from the list above.
Next step
Learn to use it properly — with a certificate
The documents tell you what to check. These courses teach you how to audit and implement it, online and at your own pace.
Questions people ask
Is the ISO 27701 Data Privacy and Cybersecurity Audit Guide really free?
Yes. There is no payment and no trial. Tell us your name, work email and company once, and every document in the Free Zone is yours to download.
What format are the documents in?
This kit has 1 document in PDF format.
Can I use it inside my company?
Yes. The licence covers one organisation with unlimited internal use — print it, share it with colleagues and adapt it. Please do not resell it or republish it as your own.
Does this make us compliant with ISO/IEC 27701?
No document can do that on its own. It is a practical working tool to help you prepare, check and improve. Conformity with ISO/IEC 27701 is decided by an audit of your actual system, and the standard itself remains the authoritative text.
Do you offer training on this topic?
Yes. Skedmia runs online courses with certificates on the standards and topics these kits cover — the matching courses are listed on this page.
More from the Free Zone
 FreeNewEditable
Cyber Security Risk Mitigation Checklist
80 controls in 10 risk areas, each with the reason it matters — plus a 5 × 5 cyber risk register template.
 FreeNewEditable
AWS Security Checklist
90 checks to review an AWS account — root user, IAM, network, S3 and databases, encryption, logging, detection and recovery.
 FreeNewEditable
IT Security Audit Checklist
120 audit checks across 12 control areas, plus an audit plan and findings log — ready for your next internal IT audit.