Free kit
Supply Chain Security Assessment Checklist (ISO 28000)
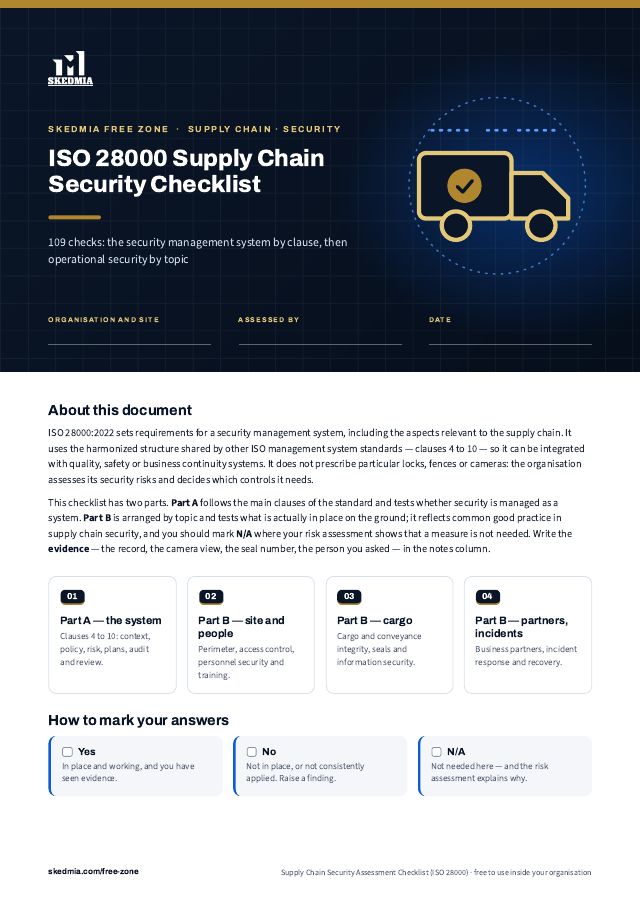
A two-part security assessment: the ISO 28000:2022 management system by clauses 4 to 10, then operational security on the ground, from the perimeter fence to the container seal.
A working checklist for assessing security in a supply chain operation — a warehouse, a freight forwarder, a transport fleet, a manufacturer that ships its own goods. It looks at security twice: first as a management system, following the clauses of ISO 28000:2022, and then as it exists on the ground, topic by topic, where an assessor can walk, look and test.
What is inside
ISO 28000 Supply Chain Security Checklist — 109 checks in 12 sections. Part A has 35 checks on the management system across clauses 4 to 10. Part B has 74 operational checks covering premises and perimeter, access control, personnel security and training, cargo and conveyance integrity, seals, information and IT security, business partners, and incident response and recovery.
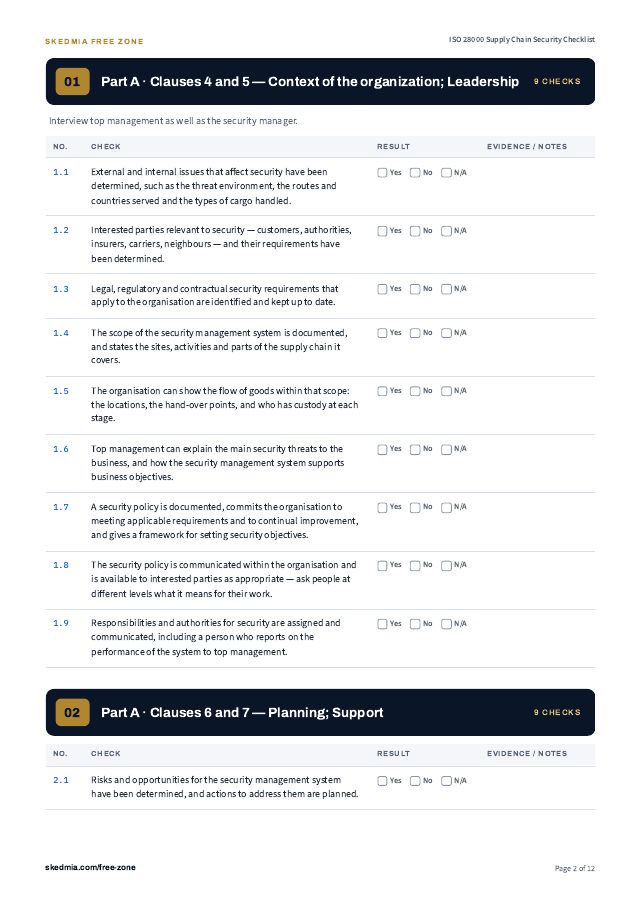
Every check is written as a statement you can find evidence for, with Yes / No / N/A boxes, space for the evidence you saw and a score summary by section.
A designed, print-ready PDF and an editable Word file.
Who it is for
Security managers, logistics and warehouse managers, internal auditors, compliance teams and consultants; organisations preparing for ISO 28000 certification or for a customer's supply chain security audit; and buyers who want a structured way to assess a carrier or warehouse.
How to use it
Use Part A in the office with management and the documented system, and Part B on site. Walk the perimeter, stand at the gate, watch a vehicle being loaded and sealed, and ask people what they would do if something looked wrong. Record what you saw, not what you were told. For every No, raise a finding with an owner and a date, and feed it back into the security risk assessment.
Clause references are to the main clauses of ISO 28000:2022 only. Part B is good practice arranged by topic, not a list of requirements from the standard: which measures you need depends on your own security risk assessment, your customers and the legal requirements that apply to you.
What is in the kit
- ISO 28000 Supply Chain Security Checklist (PDF)109 checks in 12 sections: Part A follows clauses 4–10 of ISO 28000:2022, Part B covers operational security from perimeter to seals. Yes / No / N/A boxes.1.2 MB
- ISO 28000 Supply Chain Security Checklist (editable Word)The same document in Word, so you can adapt it and fill it in on screen.36 KB
A look inside
The first pages of ISO 28000 Supply Chain Security Checklist (PDF). The full document downloads from the list above.
Next step
Learn to use it properly — with a certificate
The documents tell you what to check. These courses teach you how to audit and implement it, online and at your own pace.
Questions people ask
Is the Supply Chain Security Assessment Checklist (ISO 28000) really free?
Yes. There is no payment and no trial. Tell us your name, work email and company once, and every document in the Free Zone is yours to download.
What format are the documents in?
This kit has 2 documents in PDF and DOCX format. The Word, Excel or PowerPoint files are fully editable, so you can adapt them to your organisation.
Can I use it inside my company?
Yes. The licence covers one organisation with unlimited internal use — print it, share it with colleagues and adapt it. Please do not resell it or republish it as your own.
Does this make us compliant with ISO 28000?
No document can do that on its own. It is a practical working tool to help you prepare, check and improve. Conformity with ISO 28000 is decided by an audit of your actual system, and the standard itself remains the authoritative text.
Do you offer training on this topic?
Yes. Skedmia runs online courses with certificates on the standards and topics these kits cover — the matching courses are listed on this page.
More from the Free Zone
 FreeNewEditable
Cyber Security Risk Mitigation Checklist
80 controls in 10 risk areas, each with the reason it matters — plus a 5 × 5 cyber risk register template.
 FreeNewEditable
AWS Security Checklist
90 checks to review an AWS account — root user, IAM, network, S3 and databases, encryption, logging, detection and recovery.
 FreeNewEditable
IT Security Audit Checklist
120 audit checks across 12 control areas, plus an audit plan and findings log — ready for your next internal IT audit.