Free kit
Attack Methods and Cybercrime: CISA Exam Prep & Audit Assurance Kit
A CISA-focused guide to fraud risk, computer crime, attack vectors, malware, ransomware, and the audit evidence that proves controls work.
This kit provides a structured, exam-oriented and audit-focused guide to attack methods and cybercrime. It is built around the CISA exam perspective: what the IS auditor should do first, what the greatest concern is, and which evidence is best.
What is inside:
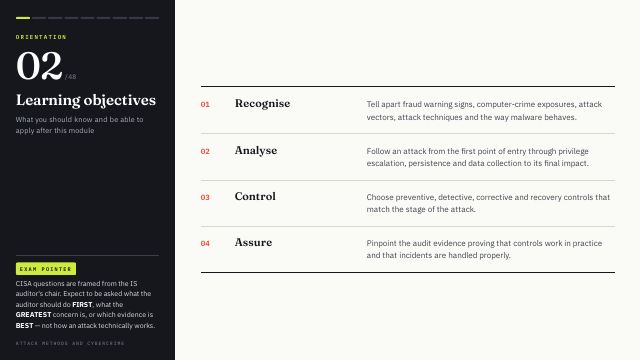
Learning objectives: recognise, analyse, control, and assure
CISA exam mapping: Domains 4 and 5 account for 52% of the exam, and this topic appears in both
The threat-to-impact chain: threat actor, attack vector, weakness, technique, compromise, business impact
Threat actors and motives: cybercriminal, insider, nation state/APT, hacktivist/opportunist
Computer crime exposures: access misuse, data/IP theft, fraud and extortion, disruption and sabotage
Legal and investigative challenges: attribution, jurisdiction, evidence, reporting
Fraud risk factors: the fraud triangle (incentive/pressure, opportunity, rationalisation)
Fraud indicators in technology processes and control responses
The path of a fraud event: prepare, deceive, authorise, execute, conceal, benefit
Fraud controls by purpose: prevent/deter, detect, correct/recover, compensate
The IS auditor’s role when irregularities surface: consider, communicate, stay in role, protect independence
The attack lifecycle: reconnaissance, initial access, execution, persistence, escalation, impact
Attack vectors: email, web/apps, credentials, network/wireless, supply chain/cloud, physical/removable media
Social engineering methods and manipulation cues
Credential and session attacks, MFA weaknesses, and phishing-resistant controls
Network, wireless, remote-access, and application attack methods with primary controls
Internet threats, business email compromise (BEC), cloud and supply-chain attacks
Insider attack methods and joiner-mover-leaver controls
Malware families, persistence techniques, classic attack terms, and the malware infection chain
Ransomware and data extortion: campaign stages, controls, RPO/RTO, response priorities, and the ransom payment decision
Cyber incident response aligned to NIST CSF 2.0: govern, identify, protect, detect, respond, recover
Evidence preservation: order of volatility, integrity, chain of custody, legal control
Choosing controls by attack stage and audit focus: governance, control design, operating effectiveness, improvement
Audit evidence and tests, common audit red flags, scenario workshop, recall map, and knowledge-check questions with answers
Who it is for
CISA candidates, IS auditors, IT risk and compliance professionals, cybersecurity analysts, fraud investigators, incident responders, and governance teams.
How to use it
Use this kit as a CISA exam revision guide, an audit planning reference, a fraud and cybercrime awareness training deck, and a practical checklist for control design, evidence collection, and incident response readiness.
What is in the kit
- Attack Methods and Cybercrime608 KB
A look inside
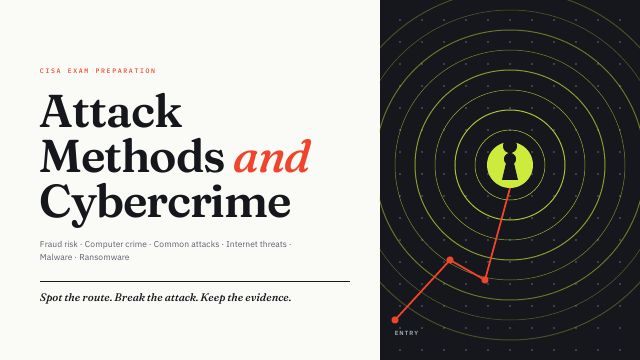
The first pages of Attack Methods and Cybercrime. The full document downloads from the list above.
Questions people ask
Is the Attack Methods and Cybercrime: CISA Exam Prep & Audit Assurance Kit really free?
Yes. There is no payment and no trial. Tell us your name, work email and company once, and every document in the Free Zone is yours to download.
What format are the documents in?
This kit has 1 document in PDF format.
Can I use it inside my company?
Yes. The licence covers one organisation with unlimited internal use — print it, share it with colleagues and adapt it. Please do not resell it or republish it as your own.
Does this make us compliant with CISA / ISACA / NIST CSF 2.0 / NIST SP 800-61 / ITAF?
No document can do that on its own. It is a practical working tool to help you prepare, check and improve. Conformity with CISA / ISACA / NIST CSF 2.0 / NIST SP 800-61 / ITAF is decided by an audit of your actual system, and the standard itself remains the authoritative text.
Do you offer training on this topic?
Yes. Skedmia runs online courses with certificates on the standards and topics these kits cover — the matching courses are listed on this page.
More from the Free Zone
 FreeNew
Food Safety Signs and Posters: Bilingual Hygiene, Temperature, Storage, Allergen & Safety Signage Kit
Hygiene, temperature, storage, allergens, hazards and workplace signs, in English and Arabic.
 FreeNew
Ammonia (NH₃ / R-717) Safety Masterclass: SS 683 & International Good Practice Kit
A complete industrial refrigeration safety programme — from understanding the hazard to preventing major incidents.
 FreeNew
Ammonia R-717 Safety, Standards & Depth Inspection: Compliance & Barrier Verification Kit
A technical programme for industrial refrigeration engineers, safety managers and facility operations leaders — building the knowledge and practical skills to run ammonia refrigeration systems safely,