Free kit
Detection Engineering 2026: 100 SIEM Use Cases, ATT&CK v19.2 Mapping, Tuning, Response & Validation Kit
A 40-page summary of 100 detection rules across 20 domains, with tuning, investigation, response, validation and roll-out guidance.
This kit is a condensed, practical detection-engineering library covering 100 priority use cases across 20 detection domains, ordered along the attack path. Every rule is written as portable logic (WHEN, GROUP BY, WINDOW, THEN) and mapped to MITRE ATT&CK v19.2. It supports ISO/IEC 27001:2022 logging, monitoring and incident-management controls, and ISO/IEC 27035 incident-handling practice.
What is inside:
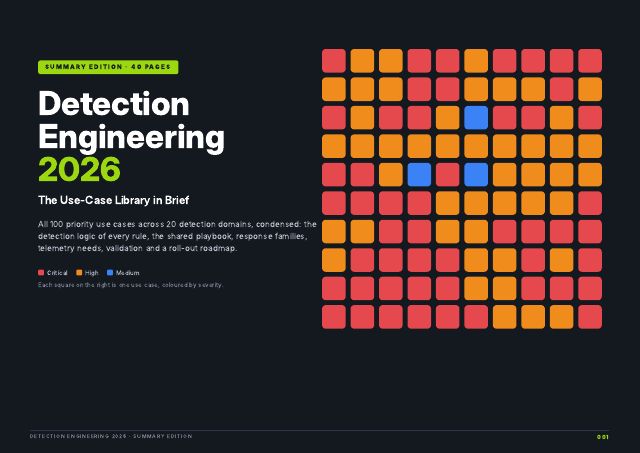
How to read the library: the 100 use cases (51 Critical, 46 High, 3 Medium), and how to trace a rule from technique to strategy, analytic, data component and your own log source.
Standard playbook
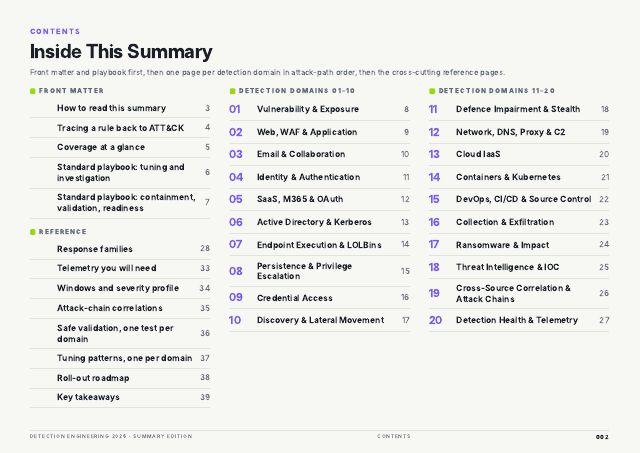
tuning controls T1–T3 investigation steps I-1 to I-7 careful versus fast containment stances five safe-validation outcomes readiness gate R-1 to R-6 20 detection domains, 5 rules each: exposure, web and application, and email identity, SaaS/M365 and Active Directory/Kerberos endpoint execution, persistence and credential access lateral movement, defence impairment and network/C2 cloud IaaS, containers/Kubernetes and CI/CD exfiltration, ransomware and IOC attack chains and detection health Each rule shows its condition, ATT&CK technique, window and severity. Response families and attack chains: 10 response families with post-confirmation actions, plus five multi-stage chains (phishing to sign-in, credential access to privileged login, EDR impairment to lateral movement, archive to upload, ransomware pre-impact). Reference pages: telemetry map, window and severity profile, safe validation tests, tuning patterns, roll-out roadmap and 12 key takeaways.
Who it is for: SOC analysts, detection engineers, threat hunters, incident responders, SIEM and EDR engineers, security architects and security managers.
How to use it: use it as a rule catalogue, a SIEM roll-out plan, a tuning and validation guide, a coverage-gap review and a SOC training reference. It helps teams build detections with an owner, proven telemetry, safe tests and a clear response, so alerts can be trusted when it matters.
What is in the kit
- Detection Engineering 2026 Summary1.2 MB
A look inside
The first pages of Detection Engineering 2026 Summary. The full document downloads from the list above.
Next step
Learn to use it properly — with a certificate
The documents tell you what to check. These courses teach you how to audit and implement it, online and at your own pace.
Questions people ask
Is the Detection Engineering 2026: 100 SIEM Use Cases, ATT&CK v19.2 Mapping, Tuning, Response & Validation Kit really free?
Yes. There is no payment and no trial. Tell us your name, work email and company once, and every document in the Free Zone is yours to download.
What format are the documents in?
This kit has 1 document in PDF format.
Can I use it inside my company?
Yes. The licence covers one organisation with unlimited internal use — print it, share it with colleagues and adapt it. Please do not resell it or republish it as your own.
Does this make us compliant with MITRE ATT&CK v19.2 · ISO/IEC 27001:2022 (A.8.15, A.8.16, A.8.17, A.5.7, A.5.24–5.28) · ISO/IEC 27002:2022 · ISO/IEC 27035 · ISO/IEC 27037 · ISO/IEC 27004 · ISO 22301 · ISO/IEC 27017 · CISA KE?
No document can do that on its own. It is a practical working tool to help you prepare, check and improve. Conformity with MITRE ATT&CK v19.2 · ISO/IEC 27001:2022 (A.8.15, A.8.16, A.8.17, A.5.7, A.5.24–5.28) · ISO/IEC 27002:2022 · ISO/IEC 27035 · ISO/IEC 27037 · ISO/IEC 27004 · ISO 22301 · ISO/IEC 27017 · CISA KE is decided by an audit of your actual system, and the standard itself remains the authoritative text.
Do you offer training on this topic?
Yes. Skedmia runs online courses with certificates on the standards and topics these kits cover — the matching courses are listed on this page.
More from the Free Zone
 FreeNew
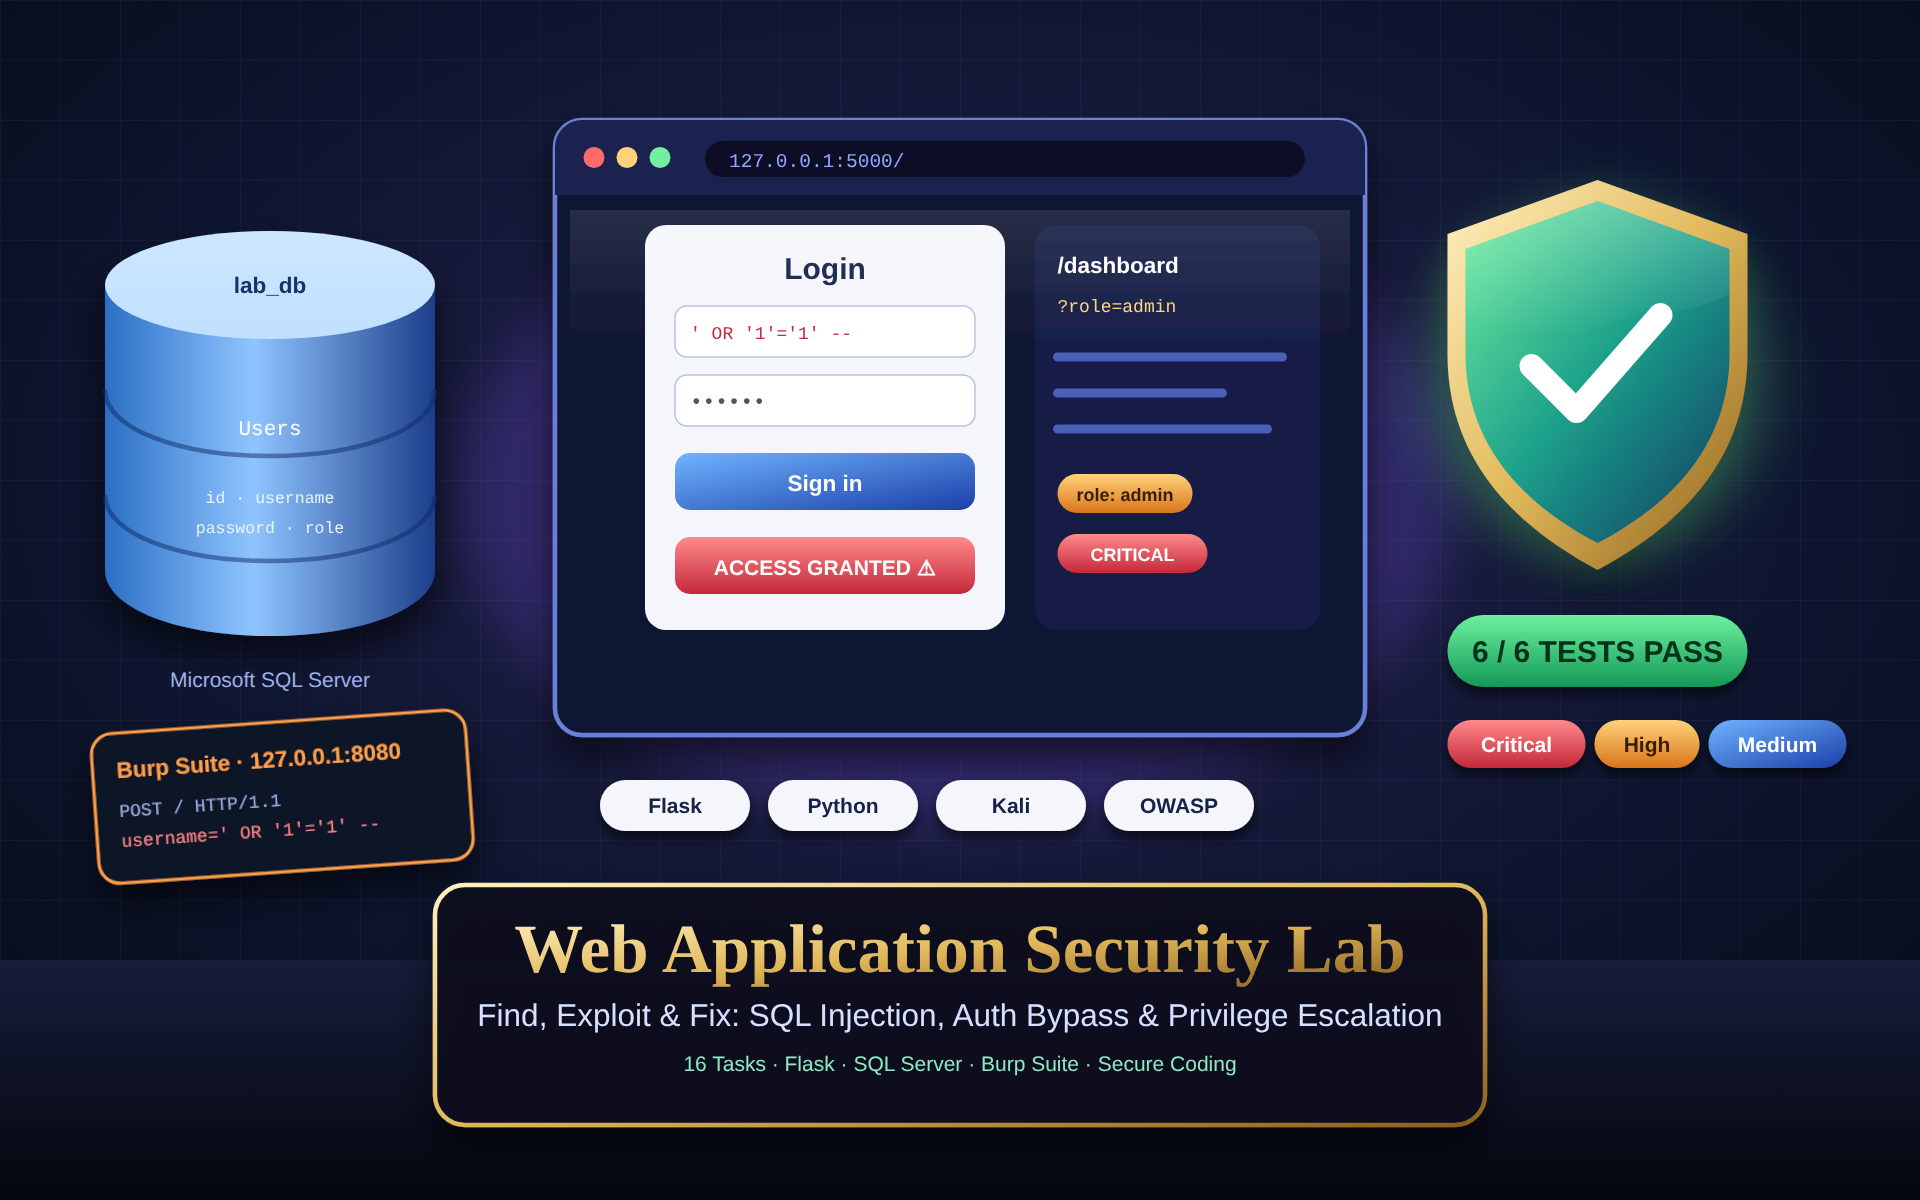
Web Application Security Lab: Find, Exploit & Fix SQL Injection, Authentication Bypass & Privilege Escalation (Flask, SQL Server, Burp Suite)
A hands-on lab report that builds a deliberately weak Flask login app, attacks it four ways, then fixes and re-tests it with secure coding.
 FreeNew
SOC Analyst (L1) Masterclass: Triage Method, 10 Incident Scenarios, 11 Labs & 111 Interview Questions Kit
A condensed SOC analyst handbook that takes a new analyst from SOC basics and alert triage to incident scenarios, hands-on labs and interview readiness.
 FreeNew
Cryptographic Controls Study Deck
A CISA Domain 5 study deck on cryptographic controls, covering techniques, PKI, key management and audit evidence, with practice questions.