Free kit
GRC Vocabulary Glossary
Plain-English glossary of governance, risk, compliance, audit, information security, quality, ITSM, privacy and business continuity terms.
P R I M A R Y C O V E R A G E ISO 9000/9001 · ISO/IEC 20000-1 · ISO/IEC 27001/27002/27005/27017/27018 · ISO/IEC 27701 · ISO 22301 · ISO 31000 · ISO 37301 · ISO 37001 · ISO 37002 · ISO 19011 · ISO/IEC 17021-1 · ISO/IEC 17011 · ISO/IEC 42001 · SOC 1/SOC 2 · AICPA Trust Services Criteria · NIST CSF · NIST SP 800 concepts · CIS Controls · PCI DSS · GDPR · DPDPA · HIPAA · CMMI/CMMI-SVC and broader GRC vocabulary.
What is in the kit
- GRC Vocabulary Glossary — All Standards73-page reference glossary. Meanings are learning paraphrases; check authoritative wording in the governing standard.1.6 MB
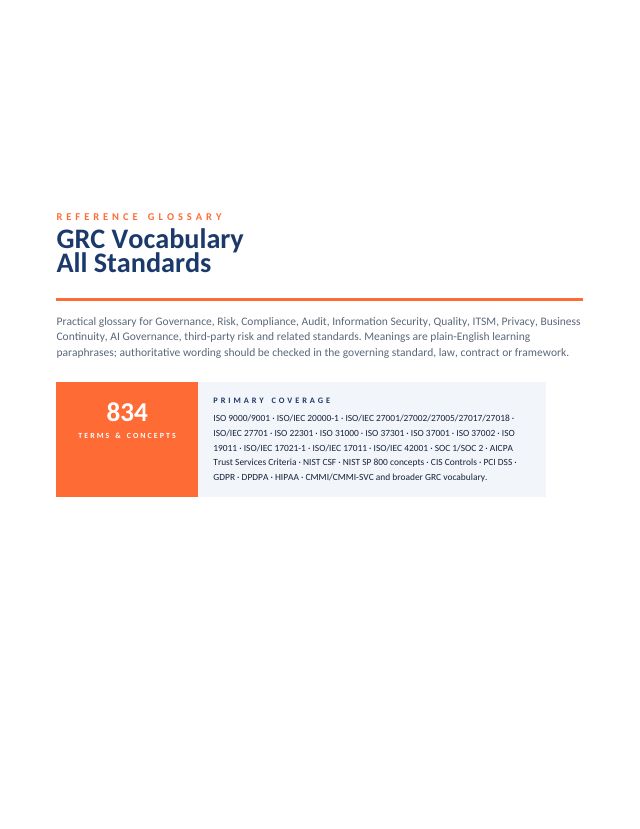
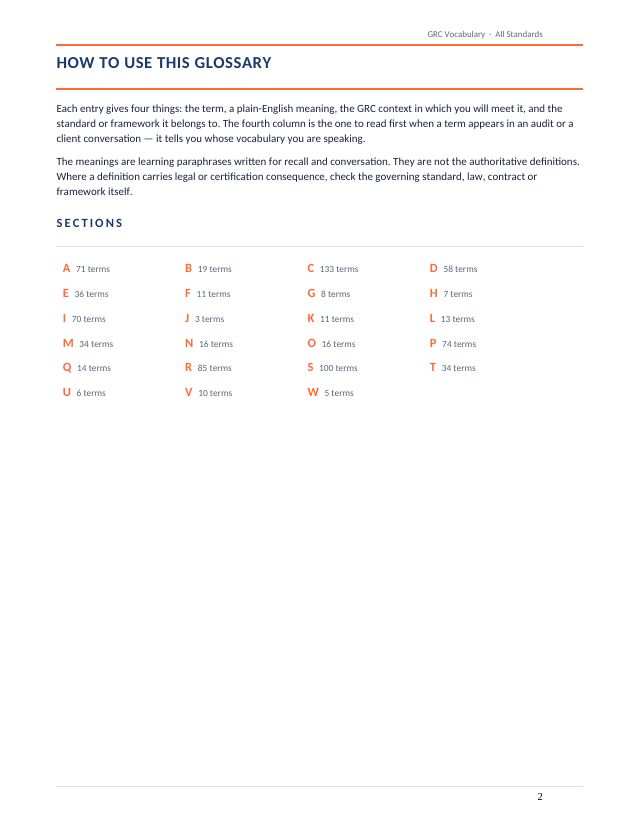
A look inside
The first pages of GRC Vocabulary Glossary — All Standards. The full document downloads from the list above.
Next step
Learn to use it properly — with a certificate
The documents tell you what to check. These courses teach you how to audit and implement it, online and at your own pace.
Questions people ask
Is the GRC Vocabulary Glossary really free?
Yes. There is no payment and no trial. Tell us your name, work email and company once, and every document in the Free Zone is yours to download.
What format are the documents in?
This kit has 1 document in PDF format.
Can I use it inside my company?
Yes. The licence covers one organisation with unlimited internal use — print it, share it with colleagues and adapt it. Please do not resell it or republish it as your own.
Does this make us compliant with GRC?
No document can do that on its own. It is a practical working tool to help you prepare, check and improve. Conformity with GRC is decided by an audit of your actual system, and the standard itself remains the authoritative text.
Do you offer training on this topic?
Yes. Skedmia runs online courses with certificates on the standards and topics these kits cover — the matching courses are listed on this page.
More from the Free Zone
 FreeNewEditable
Cyber Security Risk Mitigation Checklist
80 controls in 10 risk areas, each with the reason it matters — plus a 5 × 5 cyber risk register template.
 FreeNewEditable
AWS Security Checklist
90 checks to review an AWS account — root user, IAM, network, S3 and databases, encryption, logging, detection and recovery.
 FreeNewEditable
IT Security Audit Checklist
120 audit checks across 12 control areas, plus an audit plan and findings log — ready for your next internal IT audit.