Free kit
ISO 27701 PIMS Audit Checklist and Records
An internal audit checklist for a privacy information management system built on ISO/IEC 27701, with the records a PIMS has to keep: processing register, PIA register, rights-request and breach logs.
A working kit for auditing and running a privacy information management system (PIMS) to ISO/IEC 27701. The checklist follows the PIMS from scope and leadership through privacy risk, the statement of applicability, controller and processor duties, rights requests, breaches and improvement, so every finding can be traced to a requirement. The records document gives you the registers an auditor asks to see first.
What is inside
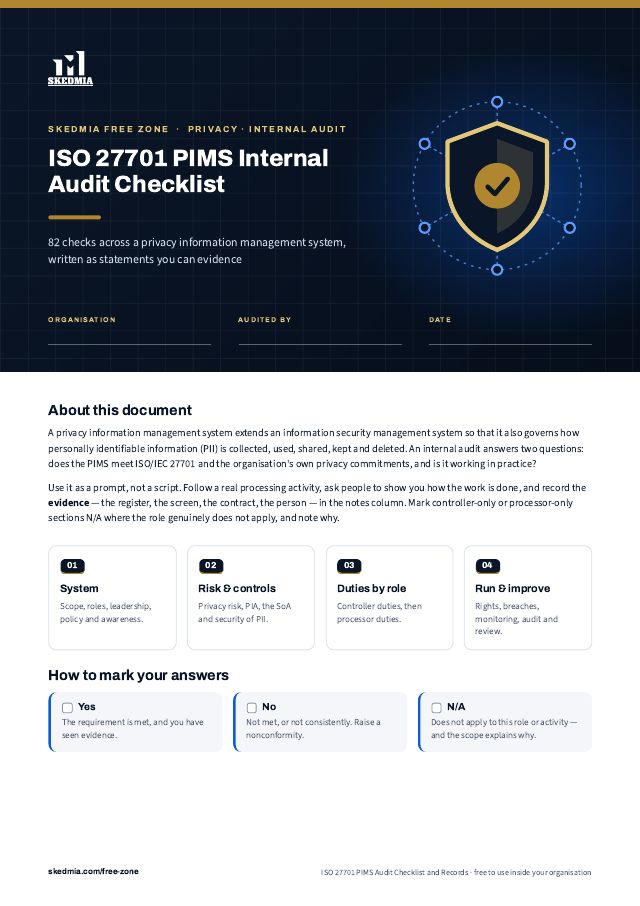
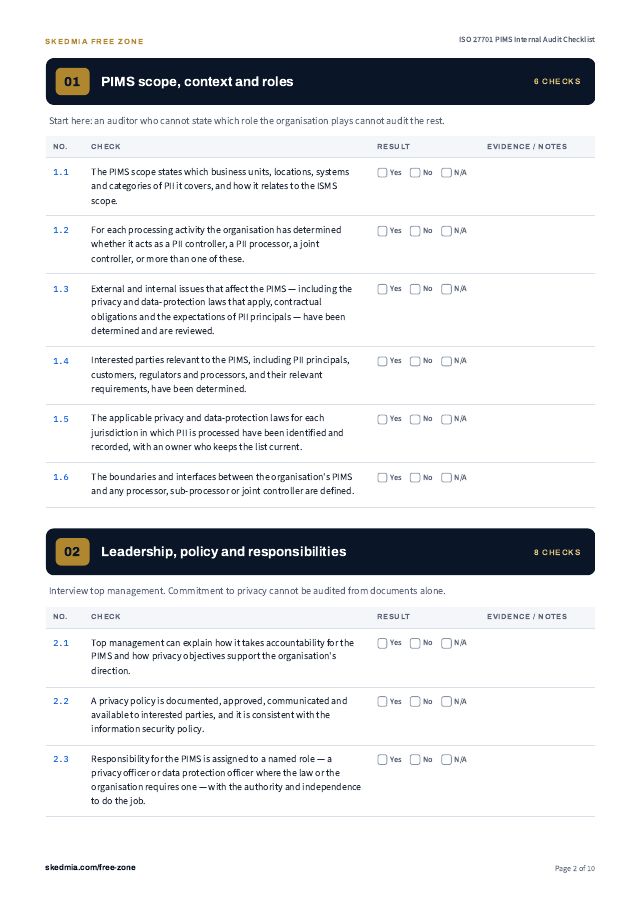
ISO 27701 PIMS Internal Audit Checklist — 82 checks across the PIMS, each written as a statement you can find evidence for, with Yes / No / N/A boxes and space for the evidence you saw.
PIMS Records Templates — scope and roles register, record of processing activities, privacy impact assessment screening and register, data subject request log, personal data breach log, processor and third-party register, and a PIMS statement of applicability extract.
Both documents as a designed, print-ready PDF and as an editable Word file.
Who it is for
Privacy officers and data protection officers, information security managers extending an ISO/IEC 27001 system to privacy, internal auditors, and consultants preparing an organisation for an ISO/IEC 27701 certification or surveillance audit.
How to use it
Audit by processing activity, not by clause: pick one activity from the record of processing, follow the personal data from collection to deletion, and use the checklist to make sure no requirement is missed along the way. Decide first whether the organisation acts as a PII controller, a PII processor or both for that activity, because different sections of the checklist apply. Record evidence for every check, and for each No write a nonconformity that states the requirement, the evidence and why it does not conform.
ISO/IEC 27701 has been revised since its 2019 edition. Check which edition applies to you and which edition your certification body audits against. Nothing in this kit is legal advice: check the privacy and data-protection laws that apply to your organisation.
What is in the kit
- ISO 27701 PIMS Internal Audit Checklist (PDF)82 checks across the PIMS — scope, leadership, privacy risk, SoA, controller and processor duties, rights, breaches, improvement — with Yes / No / N/A boxes.1.1 MB
- PIMS Records Templates (PDF)The registers an ISO/IEC 27701 auditor asks for first: processing record, PIA screening and register, rights-request log, breach log, processor register, SoA extract.684 KB
- ISO 27701 PIMS Internal Audit Checklist (editable Word)The same document in Word, so you can adapt it and fill it in on screen.34 KB
- PIMS Records Templates (editable Word)The same document in Word, so you can adapt it and fill it in on screen.30 KB
A look inside
The first pages of ISO 27701 PIMS Internal Audit Checklist (PDF). The full document downloads from the list above.
Next step
Learn to use it properly — with a certificate
The documents tell you what to check. These courses teach you how to audit and implement it, online and at your own pace.
Questions people ask
Is the ISO 27701 PIMS Audit Checklist and Records really free?
Yes. There is no payment and no trial. Tell us your name, work email and company once, and every document in the Free Zone is yours to download.
What format are the documents in?
This kit has 4 documents in PDF and DOCX format. The Word, Excel or PowerPoint files are fully editable, so you can adapt them to your organisation.
Can I use it inside my company?
Yes. The licence covers one organisation with unlimited internal use — print it, share it with colleagues and adapt it. Please do not resell it or republish it as your own.
Does this make us compliant with ISO/IEC 27701?
No document can do that on its own. It is a practical working tool to help you prepare, check and improve. Conformity with ISO/IEC 27701 is decided by an audit of your actual system, and the standard itself remains the authoritative text.
Do you offer training on this topic?
Yes. Skedmia runs online courses with certificates on the standards and topics these kits cover — the matching courses are listed on this page.
More from the Free Zone
 FreeNew
Food Safety Signs and Posters: Bilingual Hygiene, Temperature, Storage, Allergen & Safety Signage Kit
Hygiene, temperature, storage, allergens, hazards and workplace signs, in English and Arabic.
 FreeNew
Ammonia (NH₃ / R-717) Safety Masterclass: SS 683 & International Good Practice Kit
A complete industrial refrigeration safety programme — from understanding the hazard to preventing major incidents.
 FreeNew
Ammonia R-717 Safety, Standards & Depth Inspection: Compliance & Barrier Verification Kit
A technical programme for industrial refrigeration engineers, safety managers and facility operations leaders — building the knowledge and practical skills to run ammonia refrigeration systems safely,